 Ask AI
Content provenance and authenticity (Beta)
Last updated: Sep-24-2026
Introduction
The Coalition for Content Provenance and Authenticity (C2PA) is a collaboration among tech and media companies to combat online misinformation. It aims to establish standards and tools for verifying the authenticity of digital media, such as images and videos, by capturing and preserving information about their creation and editing. The goal is to prevent the spread of deceptive or manipulated content on the internet.
C2PA defines a specification to accomplish this goal. The tooling used to implement C2PA is provided by the Content Authenticity Initiative (CAI), which consists of various SDKs, a command-line tool, and an underlying Rust library. See the GitHub repo.
C2PA uses cryptography to bind provenance metadata, called assertions, directly to the asset binary. Together, those assertions record who created or edited an asset, which tools were used, and whether AI was involved. The resulting manifest is tamper-evident: anyone can verify the signature, and any change to the asset breaks that signature unless the asset is signed again. A manifest can still be stripped from an asset entirely, so C2PA is best understood as a transparency mechanism for cooperative participants rather than a way to prevent misuse.
Cloudinary preserves, extends, and verifies C2PA manifests across the whole media lifecycle: on upload, through transformation and optimization, and at delivery.
You can use this online validation tool to see the history of certifications that have been applied to an image.
Cloudinary and the C2PA standard
Cloudinary has been an active participant in content authenticity standards work for several years:
- Cloudinary joined the Content Authenticity Initiative (CAI) in December 2020 and supports the adoption of open standards for media provenance and authenticity.
- Since 2023, Cloudinary has been included on the C2PA Interim Trust List (ITL) as an early supporting service, and is progressing through the official C2PA Conformance Program.
- Cloudinary is a member of ISO/JPEG and participates in the JPEG Trust work on ISO/IEC 21617, which sets standards for trustworthy media.
- Cloudinary holds U.S. Patent US 11,550,879 B2, "Providing Authenticity Mechanism for Media Content".
Scope
C2PA in Cloudinary is currently available only to customers who request it. To use the capabilities described on this page, contact our support team to have them enabled for your product environment.
It's implemented for images only (specifically, these output formats: avif, heic, heif, jpg, jpeg, png, svg, tif, tiff, and webp).
Cloudinary adds its signature in a new manifest on top of any existing manifests. If a previous signature is invalid, Cloudinary also marks the previous manifest as invalid.
Alterations made by Cloudinary are classified as transcoded or edited. The transcoded actions are defined by a closed allowlist and include: c_fit, c_mfit, c_pad, c_lpad, c_mpad, f_*, q_*, and c_scale with a single dimension, w or h.
All other actions are classified as edited.
The metadata attached to each asset contains the certificate, a private key, and a timestamp.
-
Video and other formats: support for
mp4andjxlis planned. - Backfilling existing assets: C2PA applies to assets you upload and deliver after the feature is enabled. There's no bulk process for adding manifests to assets already stored in your product environment.
- Remote manifests: manifests are currently embedded in the asset. As a manifest accumulates assertions over an asset's lifetime it grows, which adds to the delivered file size. Support for remote manifests, which keep the manifest separate from the asset so that day-to-day delivery stays light, is planned.
How Cloudinary adds C2PA manifests
Cloudinary adds C2PA manifests in two automatic cases and one on-demand case.
| Case | Trigger | What Cloudinary does |
|---|---|---|
| Preserve provenance | An uploaded asset already contains a valid C2PA manifest. | Cloudinary preserves the existing manifest and carries the provenance chain forward to the derived asset on delivery, signing its own actions into a new manifest. |
| Start the chain for generative AI | A transformation uses generative AI. See the full list. | Cloudinary injects a manifest marking the derived asset as AI-altered, starting a provenance chain even if the original had no manifest. |
| On-demand assertion | You add the c2pa flag (fl_c2pa) to a delivery URL. |
Cloudinary signs the derived asset and adds a manifest, whether or not the original contained one. |
Preserving an existing manifest
When an asset that already carries C2PA credentials is uploaded, Cloudinary preserves the assertion manifest and carries it forward at delivery, so a chain that began in a camera or a creative tool isn't broken by transformation and optimization.
Starting a chain for generative AI transformations
Any transformation that uses generative AI produces an asset that has been materially altered by AI. For those transformations, Cloudinary dynamically injects a manifest recording that AI altered the asset. This means a derived asset carries a machine-readable record of the AI involvement without you needing to add anything to the URL.
The following transformations start a provenance chain:
-
Background removal (
e_background_removal) -
Content extraction (
e_extract) -
Drop shadow (
e_dropshadow) -
Generative background replace (
e_gen_background_replace) -
Generative fill (
b_gen_fillwithc_pad) -
Generative recolor (
e_gen_recolor) -
Generative remove (
e_gen_remove) -
Generative replace (
e_gen_replace)
Requesting a manifest on demand
When delivering images that you want to be signed by Cloudinary, include the c2pa flag, (fl_c2pa in URLs). For example:
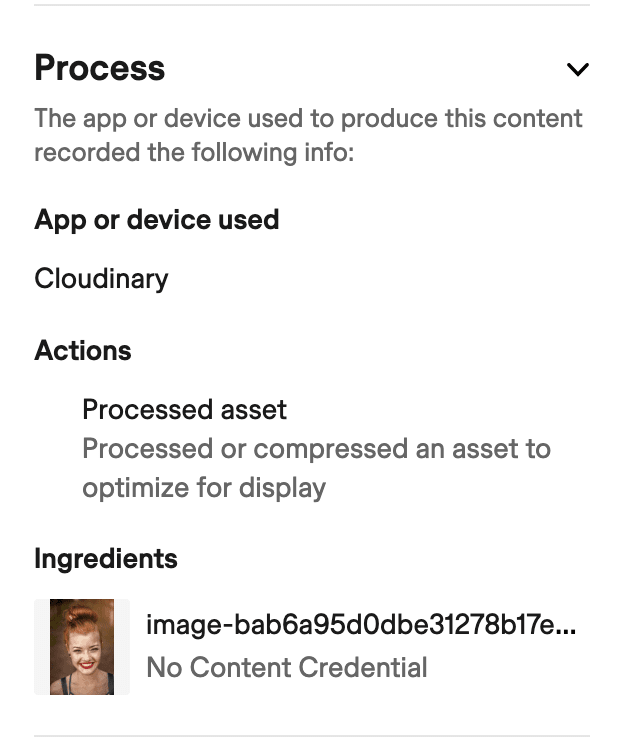
For images that are transcoded but not edited, for example c_scale,w_550/fl_c2pa, a validation tool would show something similar to the following (view in validation tool):

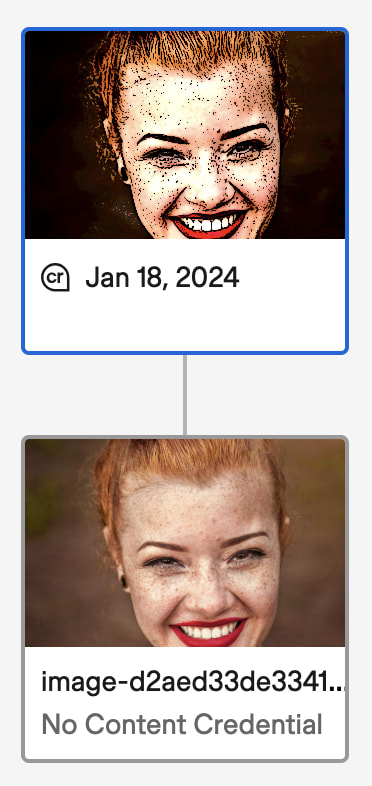
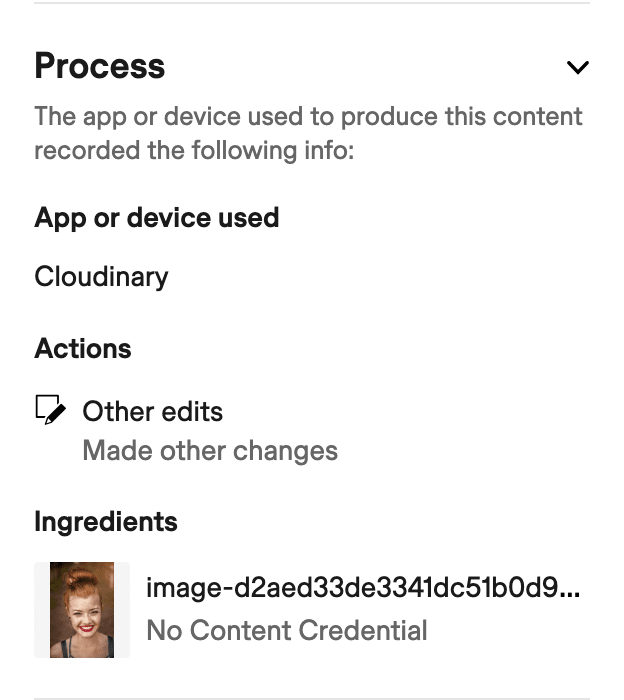
For images that are edited, whether or not they're also transcoded, for example e_cartoonify/fl_c2pa, a validation tool would show something similar to the following (view in validation tool):
Provenance and AI fields
Alongside the manifests themselves, Cloudinary tracks two asset properties: whether AI was involved, and whether the asset carries a manifest at all. A manifest on its own doesn't mean AI was used, so the two are independent. They also work differently from each other:
| Field | Values | Description |
|---|---|---|
| AI-generated |
true / false
|
Whether AI generated or altered the asset. Set on upload, read from an incoming C2PA manifest, or set by Cloudinary when it generates an image. |
| Has C2PA |
true / false
|
Whether the asset carries a C2PA manifest. Cloudinary sets this itself by inspecting the file, so you never set it. |
The AI-generated flag is stored as a virtual contextual metadata field. Cloudinary stores it as contextual metadata, but in a private block that's separate from the contextual metadata you set yourself, so it doesn't appear alongside your own keys and you can't overwrite it by accident. Because it's a context field, you can reference it in conditional transformations, which is what makes a visible AI disclosure possible.
The field is protected from tampering, so you can't set the underlying context key directly. To mark an asset as AI-generated, use the dedicated ai_generated upload parameter.
Has C2PA is a property that Cloudinary derives from the asset itself. It isn't contextual metadata, so you can't use it in a conditional transformation.
Both fields are available in search expressions.
Field names
The name you use depends on where you're using the field:
| Context | AI-generated | Has C2PA |
|---|---|---|
| Upload parameter | ai_generated |
Not applicable: set by Cloudinary |
| Search expression | ai_generated |
has_c2pa |
| Conditional transformation | cld_ai_generated |
Not applicable: not a context field |
The conditional transformation variable carries a cld_ prefix because it's read from contextual metadata, where it could otherwise clash with a contextual metadata key of the same name that you've defined yourself. The prefix keeps the two apart, so the result is never ambiguous.
How the AI-generated flag gets set
The AI-generated flag can be set in several ways:
-
By you, on upload: pass the
ai_generatedupload parameter in your upload call. - By Cloudinary, from an existing manifest: when an uploaded asset contains a C2PA manifest, Cloudinary inspects the manifest and sets the flag if the manifest indicates the content was AI-generated.
- By Cloudinary, on AI generation: when you generate an image with Cloudinary's generative AI capabilities, Cloudinary sets the flag on the result.
Setting ai_generated on upload is useful when you're bringing in AI-generated assets in bulk from a generation pipeline, where you already know the assets are AI-generated and the source files may carry no manifest.
For example, uploading an AI-generated image and marking it as such:
Finding assets by provenance
Both fields are available as search expression parameters, so you can find assets by their provenance using the Search API or the Media Library search. For example, to find all AI-generated assets:
Or to find assets that don't yet carry a C2PA manifest:
Disclosing AI-generated content
Regulations such as the EU AI Act require transparency when AI-generated media is published. Article 50 of the EU AI Act sets out two distinct obligations, and meeting them calls for two different mechanisms:
| Audience | Requirement | How Cloudinary helps |
|---|---|---|
| Machine-to-machine | Search engines, scrapers, browsers, and social networks can read and inspect content history programmatically. | Cloudinary signs and adds C2PA assertions containing provenance metadata to the asset. The manifest travels with the asset across CDNs. |
| Machine-to-human | People viewing the media can easily tell when it's AI-generated or AI-altered. | Conditional transformations overlay a visible disclosure on the asset when cld_ai_generated is true, applied at delivery rather than burned into the original. |
Using Cloudinary's C2PA and AI disclosure capabilities doesn't by itself make you compliant with the EU AI Act or any other regulation. Cloudinary provides technical capabilities that support transparency requirements, but you remain responsible for your own legal compliance. Consult your legal or compliance team about which obligations apply to you.
Adding a visible AI disclosure
To disclose AI generation to people viewing your assets, use a conditional transformation that overlays a logo only when the asset's AI-generated flag is true. Assets that aren't AI-generated are delivered unchanged, so you can apply the same transformation across your whole library.
The following transformation overlays the logos:AIGenLogo image, sized to 10% of the asset width, in the bottom-right corner, but only when cld_ai_generated is true:
Because the overlay is applied at delivery, you control its size, placement, and appearance per delivery URL, and you can combine it with any other transformation. For example, cropping to a 9:16 aspect ratio and then adding the disclosure:
t_AIgenlogo, and so that you can change the disclosure's appearance in one place.Verifying a manifest
Anyone can verify the signature and provenance of a delivered asset using standard C2PA verification tools:
- The Content Credentials verification tool shows the chain of manifests in a browser. Pass the delivery URL as the
sourcequery parameter, for example this signed image. - The c2patool command-line tool inspects an image file's manifests in detail.
A verification tool shows each step in the chain in order. For an asset created by a generative AI tool and then transformed by Cloudinary, the chain shows the original AI generation, any edits made in other tools, and the actions Cloudinary performed.
Error
Rate this page:
